|
Okay, I just found out passwords on bnet aren't case sensitive. This means that it doesn't matter whether your password is coolguy or CooLGuY. Battle.net treats them the same. I think it's fair to say that most services require correct typing of passwords including upper and lower cases.
Do you think it's a good idea to demand case sensitive passwords? Should we let Blizzard know about our demand? If most of you answer "yes", can someone start a proper organised thread please in order to draw Blizzard's attention? I'm not good at writing smart, so I'm kinda useless. 
Ok, there's a poll for you:
Poll: Case sensitive password?Yes (15) 58% I don't care (9) 35% No (2) 8% 26 total votes Your vote: Case sensitive password? (Vote): Yes
(Vote): No
(Vote): I don't care
Update:
+ Show Spoiler +I contacted Blizzard, and this is what I got as an answer:
Hello,
Sadly we in the GM team are not responsible for the overall account security, please keep this to the forums (you will find multiple posts on this already) however sadly even if passwords were case sensitive it would make very little difference to the amount of losses on accounts, case sensitive or not people are still getting keylogged, we are yet to come across a case of an account being brute forced.
Also blizzard passwords have been this way since the very beginning of WoW, even before.
However your concerns are noted as are the conserns of the community at large.
Regards
Korgalos
Blizzard Entertainment
Customer Services EN
  
|
What? PW's aren't case sensitive? Then why the fuck have I been doing upper and lowercase pw's...
|
I'm mostly just pissed that for all these years, there was a much simpler way of typing my password. -_- Yeah that's completely ridiculous.
|
They already offer you free authenticators. Your password could be "password" and it wouldn't matter if you used one.
|
Lol wtf why would passwords not be case sensitive.
|
Didnt know about this either, but Blizzard has my phone number to verify identity, so w/e.
Still a pretty unnecessary risk, why the hell wouldn't you make them CS?
|
wow. had no idea. blizzard what are you doing... you're almost making this too easy
|
The reason why, is that even with Authenticators being out, Blizzard has admitted to a security hole in the system allowing a hacker to bypass that phase of login. There were tons of people exploiting it to hack Diablo 3 accounts day 1. I'm not sure if it carries over into SC2, but it could be assumed considering that they share Account Information. It just brings the security up to par with most other commercial sites.
|
On May 28 2012 08:53 Micen wrote:
The reason why, is that even with Authenticators being out, Blizzard has admitted to a security hole in the system allowing a hacker to bypass that phase of login. There were tons of people exploiting it to hack Diablo 3 accounts day 1. I'm not sure if it carries over into SC2, but it could be assumed considering that they share Account Information. It just brings the security up to par with most other commercial sites.
http://eu.battle.net/d3/en/forum/topic/4309703662
In all of the individual Diablo III-related compromise cases we’ve investigated, none have occurred after a physical Battle.net Authenticator or Battle.net Mobile Authenticator app was attached to the player’s account, and we have yet to find any situation where a Diablo III player's account was accessed outside of “traditional” compromise methods (i.e. someone logging using an account's login email and password).
|
Gheed:
Blizzard has confirmed that a work-around that allows hackers to gain access to games protected by its authenticator tool has been invented.
This is the first confirmed case of a compromised World of Warcraft account with an authenticator attached. The affected user alerted others to the issue on the official forums, which was responded to by a Blizzard rep, who confirmed that the case was genuine. Other players then reported similar experiences.
Blizzard poster Kropacius informed readers that the type of problem was a ‘Man In The Middle’ attack. According to information from various affected users, the hacker gains access to a player’s system through a keylogger, thought to be a file named emcor.dll, which can be found in C:/Documents and Settings/Users/[username]/Application Data/Temp. Once infected, the PC will cause WoW to crash, prompting players to log back into the game. This is when the authenticator code is intercepted by the hacker, who sends on a different code to Blizzard’s servers, preventing the legitimate user from gaining access to the game. In the mean time, the hacker does have access to the account until the code resets, and can proceed to steal any gold and/or possessions from your characters.
The code on an authenticator changes every 30 seconds or so, therefore hackers only have access to the account until they log out. In the case of the original user who reported the issue, he was blocked from attempting to access WoW for 15 minutes after inputting “incorrect” login details too many times. During that time, the keylogger file was detected and removed. Nothing was changed in the account management on the official WoW site, but when he gained access to WoW after the lock-out, several in-game items were gone; the hacker had presumably been logged out when the owner logged back in.
Blizzard has always maintained that the authenticator was never a 100% fool-proof method of keeping game accounts safe, and should be treated as an additional layer of protection. This latest development further highlights the need to be aware of keyloggers, and to keep anti-virus software up to date. However, neither of these prevented the afore-mentioned user from falling foul of the scum of the internet.
Source: http://diablo.incgamers.com/blog/comments/first-blizzard-authenticator-hack-confirmed
Ontopic:
I do not want to use an authenticator for various personal reasons, but I do feel that the password policy of Blizzard is lacking terribly. Why can't we use special characters for example?
|
I hadn't seen that. However, that method relies on a person having a keylogger on their computer, which would render a case-sensitive password useless anyway.
|
Erm.
Oh wow that actually works.
As mentioned above, most more sophisticated methods probably make case-sensitivity useless as a security measure, but it's a very good thing to force to, idk, make it much less easily dumbass-able.
|
Is it time to link this XKCD comic?
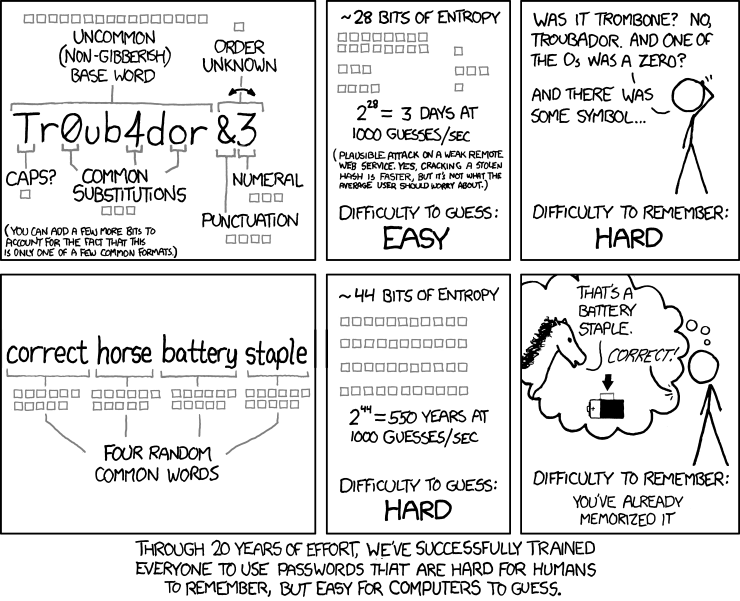
Seriously though, it's what Gheed said. Hacked accounts are basically never brute forced, and hacked accounts with authenticators, something that hasn't happened in D3 so far it seems, only in WoW, are not only much more rare but also impossible to brute force. Adding case sensitive passwords would change nothing.
Micen's post is wrong, they admited in a WoW case, but still say it hasn't happened in D3. Definatelly not "a ton of people".
|
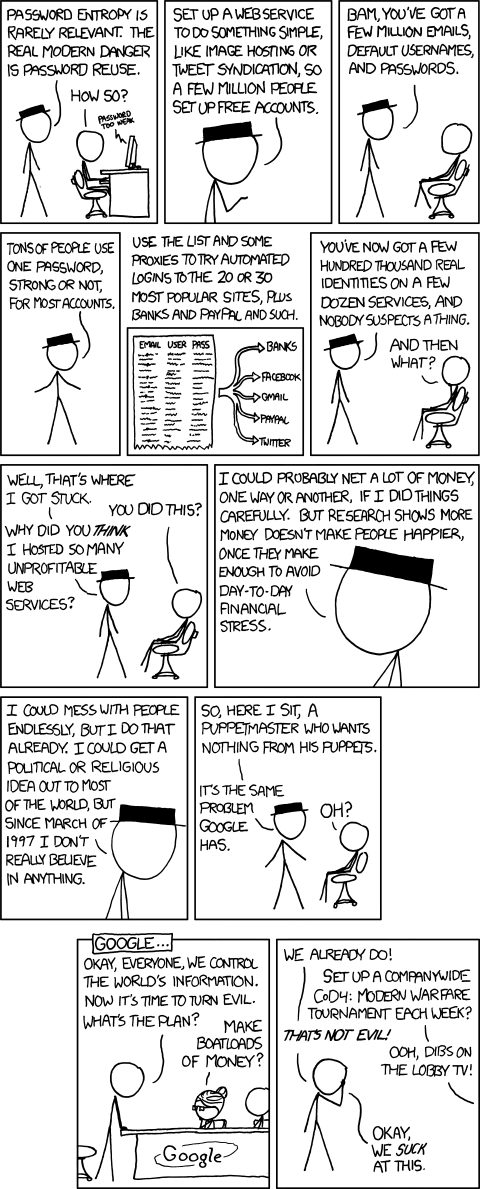
Does it actually matter? It's not like anybody can bruteforce a password even if they know its only restricted to a-z0-9, don't they kick you out after a few guesses? If you're getting hacked, your password being stronger wouldn't help you since presumably you either got keylogged or phished or something like that.
edit: here's another appropriate xkcd comic related to this 
|
Answer from Blizzard:
Hello,
Sadly we in the GM team are not responsible for the overall account security, please keep this to the forums (you will find multiple posts on this already) however sadly even if passwords were case sensitive it would make very little difference to the amount of losses on accounts, case sensitive or not people are still getting keylogged, we are yet to come across a case of an account being brute forced.
Also blizzard passwords have been this way since the very beginning of WoW, even before.
However your concerns are noted as are the conserns of the community at large.
Regards
Korgalos
Blizzard Entertainment
Customer Services EN
|
|
|
|
|
|
 EPT


